Your Employee Just Got a Sextortion Email. Is It a Security Incident?

Get reasoning, in your inbox.
Threat research and field notes from inside customer inboxes. Twice a month, no spam, unsubscribe anytime.
Keep reading .
More from the StrongestLayer team.
Threat research, customer stories, product updates, field notes from inside real inboxes.
Deep-dive analyses on AI-generated phishing, BEC, QR-code phishing, and adversary-in-the-middle attacks.
Hosted by Alan LeFort & Karen Letain. The cybersecurity shifts that actually matter, every other week.
This article examines how a seemingly personal sextortion email can cascade into an enterprise security incident. We introduce two proprietary frameworks – “Panic Attack Chain” and “False Compromise Signals” – to map the psychological and technical steps from a personal scam to organizational risk. In doing so, we cite industry research and real-world examples to demonstrate the mechanics of these attacks. Finally, we offer 6–8 practical detection and response recommendations for security teams, blending technical controls and policy measures. The goal is to provide security leaders and HR/legal stakeholders with a clear understanding of this threat and actionable guidance to mitigate it.
Sextortion scams have surged in frequency and sophistication. In these attacks, cybercriminals leverage fear and embarrassment to coerce victims into paying a ransom. Typically, the scammer claims to have hacked the victim’s webcam or obtained explicit photos or videos, often citing a real or stolen password to convince the target of their access. The FBI has warned that modern sextortion campaigns now exploit AI and deepfake technologies to fabricate “evidence” of wrongdoing, heightening the threat.
Importantly, sextortion scams often use technical ploys similar to phishing. Attackers send mass emails through compromised high-reputation accounts (e.g. Office 365 or Gmail) to bypass spam filters. These messages usually contain no malware or malicious links, relying instead on social engineering to prompt a response. Employees may receive subject lines like “Your account has been hacked – change your password” or outright threats to their privacy.
While much commentary treats sextortion as a consumer or individual problem, the workplace context changes the stakes. Modern research and incident reports indicate that employees are being targeted – and often more so than executives or infrastructure – in these blackmail campaigns. Security teams must therefore recognize that a personal sextortion email can act as an entry point for broader organizational compromise. As we explain below, the employee’s psychological response and the tactics used by attackers can create a chain of events that impacts the entire enterprise.
Sextortion Meets the Enterprise
Why should organizations care about sextortion? The answer lies in the interplay between personal and corporate security. Employees’ personal online habits, credentials, and reactions become vectors of corporate risk. For example, a 2017 breach at Zomato was traced to an employee reusing a leaked personal password on a work-related account. This highlights a key principle: personal compromise often bleeds into corporate compromise. In the context of sextortion, an extortion email might claim to have hacked a personal device, but the panic it causes can lead an employee to take actions (or fail to take actions) that expose the company.
Security research shows that employees are often targeted by sextortion even more than by traditional BEC (Business Email Compromise) schemes. One analysis found that one in 10 spear-phishing campaigns against enterprise users were sextortion or blackmail attempts. Attacks frequently impersonate internal stakeholders or use personalized details (like a known password) to appear credible. When a sextortion email lands in a corporate inbox, an employee might initially assume their work account has been breached, triggering an incident response. Alternatively, they might panic and try to handle it alone, potentially downloading unvetted “security” tools or sharing sensitive information.
This dynamic leads to our first framework, the Panic Attack Chain, which maps how a personal threat generates human responses that propagate to corporate risk. But before introducing it, consider how sextortion scams borrow from enterprise extortion. Security writer Paul Ducklin coined “breachstortion” to describe emails that mimic ransom demands by claiming a network breach. In one example, victims were told “Your site has been hacked” and pressured to pay Bitcoin or see a supposed database leak expose their reputation. Like sextortion, breachstortion lies (no real hack occurred) but exploits organizational fear of public embarrassment or regulatory fallout.
Both sextortion and breachstortion follow a common pattern: engineer a believable breach scenario, create urgency, and demand a small payment compared to the implied damage. This leads into our frameworks, which dissect the signals and reactions involved in these scams.
Framework 1: Panic Attack Chain
The Panic Attack Chain illustrates the psychological progression from receiving a sextortion email to actions that jeopardize enterprise security. It is inspired by studies of cognitive biases and emotional triggers in social engineering. The chain has several stages:
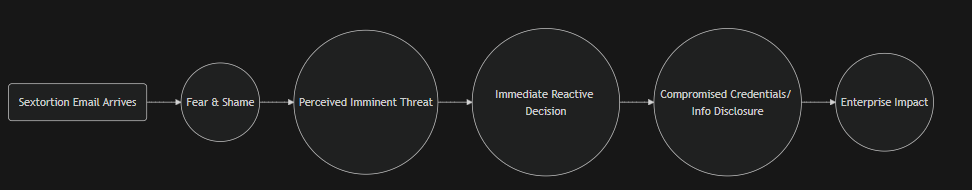
- Email: The victim receives an extortion email that appears credible. It may include personal data (e.g. a leaked password) or claims of hacking. This engineered stimulus establishes engineered legitimacy.
- Shock (Fear & Shame): The content triggers fear, embarrassment, and a loss of composure. Research shows attackers exploit emotions like fear and urgency to bypass rational judgment. The victim’s authority bias or trust is exploited if the email mimics a high-level sender, increasing shock.
- Urgency (Perceived Threat): The email imposes a deadline or threat (e.g. “24 hours or video to all contacts”). The victim perceives an imminent crisis. This leverages urgency/scarcity biases. The victim often assumes a technical breach has occurred – not realizing it’s a bluff.
- Hasty Action: Under stress, rational processes are short-circuited. Possible actions include:
- Reacting personally (e.g., contacting IT outside protocols, changing passwords hastily, or paying to silence blackmail).
- Avoiding reporting (embarrassment prevents escalation to IT).
- Seeking quick fixes (installing unauthorized apps, or even letting an unknown “consultant” in to resolve it).
- Consequences (Corporate Exposure): These reactive steps can cause direct corporate harm:
- If an employee contacts “IT” by email, they may inadvertently reply to the attacker or share internal info.
- If they change passwords on shared corporate accounts (or create new ones), they may weaken security (e.g. resetting without approval).
- If they pay or engage, it encourages further social engineering (the attack can iterate, demanding more).
- If the employee downloads a tool or clicks a link in panic, they could actually install malware.
- In some cases, fear leads to policy violations: e.g., skipping MFA, or sharing data with third parties promising help.
- Enterprise Risk: Ultimately, the chain culminates in risks like compromised credentials, unauthorized access, data leakage, or misuse of IT resources. The attacker’s goal is met by triggering these steps, even without technical hacking. As one expert notes, attackers exploit predictable human decision patterns to cause security breaches.
Example Illustration: An employee at Acme Corp receives an email claiming their personal email was hacked and a video recorded via their webcam. The email includes AcmeCorp123!, the employee’s old work password. Shocked, the employee assumes corporate systems were breached. In panic, they contact a “security vendor” (actually the attacker via a phony link), granting remote access under the pretext of investigation. This inadvertently gives the attacker a foothold in the corporate network – turning a personal sextortion attempt into a real data breach.
This chain highlights why even false threats can have real consequences. Training and awareness must address each link: employees should recognize emotional triggers and understand that an unsettling email does not equate to an actual hack.
Framework 2: False Compromise Signals
Attackers reinforce the Panic Attack Chain by planting False Compromise Signals – cues that mimic a real security incident. These signals exploit the victim’s uncertainty about what is real, deepening the panic. Our “False Compromise Signals” framework categorizes common lies and tactics used in sextortion emails and their psychological effect:
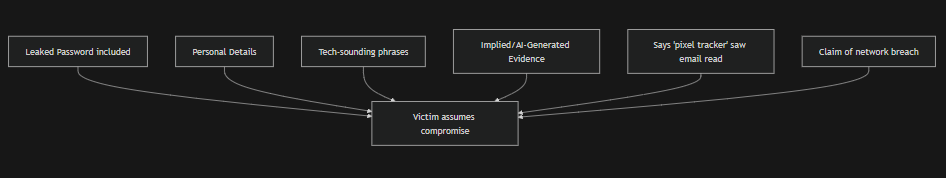
Key False Signals:
- Known Passwords: Including a real password (even if old) is a classic trick. For example, the email may open with “I know your password was X.” This instantly convinces recipients that something was indeed compromised. Victims often think, “If they have my password, maybe they breached our company too.” Studies confirm that seeing a valid password causes victims to panic and respond.
- Personal Identifiers: The attacker may include the victim’s email, phone number, job title, or last name in the message. This personalization adds engineered legitimacy: the victim feels “spotted” by a hacker. In corporate contexts, this might include titles (e.g. “Security Officer at [Company]” in the greeting) or references to the victim’s department.
- Cited Technical Details: Phrases like “hacked via your webcam”, “exploited a vulnerability”, or “we accessed your cloud drive” are inserted. These sound official and technical, preying on victims’ lack of deep IT knowledge. The email may include a snippet of code or a fake security incident report. Such jargon aims to circumvent the “lack of understanding” stage of awareness.
- Implied Multimedia Evidence: Even if not provided, the email hints at recordings or screenshots. Attackers might promise to send proof or claim to have evidence (often they never do). The mere threat of visible proof compounds panic.
- Social Proof and Deadline: Some messages mention a tracking pixel (e.g. “I know you’ve read this email”) or cite an arbitrary incident number/ticket. They set a tight deadline (“24 hours to pay”) to increase pressure. This is a common social engineering trick to avoid giving victims time to verify.
- Breach & Brand Damage Claims: In more “enterprise” versions, the email might claim a company system was hacked, data stolen, or that regulatory fines await if not resolved. The Coveware “Phantom Incident” examples illustrate this: victims were told “We have extracted your entire employee database” and warned of reputational ruin. These claims tap into corporate anxieties about data breaches.
These signals are false – no real breach has occurred – yet they cause the victim to treat the situation as if it were real. The combination of the Panic Attack Chain (emotional response) and False Compromise Signals (cues of legitimacy) is powerful.
Example: A mid-level manager at a tech company receives an email titled “URGENT: Your Company Network Compromised”. It includes the manager’s work email and the last four digits of their SSN (sold on dark web). The sender claims to have exfiltrated customer data and will inform regulators and press if not paid. Terrified at the thought of a real breach, the manager bypasses normal reporting channels and responds directly, setting off a false alarm in the company. In reality, the data snippet was harvested from LinkedIn and public sources – a false compromise signal that fueled a major enterprise incident response.
Case Studies & Real-World Examples
- Breachstortion Emails: As Sophos reported, attackers are using “breachstortion” to extort organizations by falsely claiming a hack. One sample read, “We have hacked your website and extracted your databases… We will leak it unless you pay.” This campaign used the same psychology as sextortion but aimed at IT executives. No actual breach existed, yet companies scrambled to investigate, illustrating how corporate crisis mode can be triggered by a hoax.
- Phantom Incident (Corporate PII) Scam: Security firm Coveware documented “Phantom Incident” extortion, where emails threatened to release personal data of every employee. In one case, scammers attached a small sample of stolen PII (like Social Security Numbers from public leaks) to make it seem real. They set a Bitcoin ransom framed as a fraction of the cost of a full breach. The combination of legitimate-seeming data (false signal) and low ransom preys on corporate fear of breach disclosure. These patterns mirror our frameworks: personal data inclusion triggers panic, and the “offer to buy back the data” leverages the asymmetric financial pressure.
These examples underscore that even enterprise-targeted extortion uses the same playbook: fear, urgency, and false evidence.
Detection & Response Recommendations
Security teams must treat employee-directed sextortion as a valid threat vector. Below are practical recommendations – a mix of technical controls and policies – to detect and respond when a sextortion attempt potentially impacts the organization:
- Advanced Email Filtering (Intent & Keyword Detection): Deploy or tune email gateways and anti-phishing tools to look for sextortion-specific patterns. Since these emails often lack malware, detection must rely on content. Watch for subject lines with account-compromise alerts or password references. Use AI-based filters to catch conversational cues like “webcam”, “bitcoin”, “leaked data”, etc. For example, Barracuda suggests spear-phishing defenses that include blackmail email signatures.
- Monitor for Compromised Sender Accounts: Many sextortion emails come from hijacked internal or trusted accounts. Implement Account Takeover protection: use anomalous login detection (e.g. new IPs or geographies) and frequent MFA challenges for email accounts. If a user’s account is sending unusual messages (especially with “password reset” instructions or cryptocurrency requests), quarantine outgoing email and alert admins.
- Threat Intelligence and Geolocation Filtering: Sextortion campaigns often originate overseas. Use threat feeds to block or flag emails from high-risk regions or IP ranges. Periodically review spam folder incidents for patterns. Barracuda research notes proactive searches for keyword themes (e.g. “change password”, security alerts) and geolocation of senders. Set up automated searches for suspicious phrases in delivered mail.
- Employee Awareness & Training: Incorporate sextortion scenarios into security awareness programs. Emphasize not panicking and reporting incidents to IT immediately. Simulate sample sextortion emails in phishing drills to lower the shock factor. Ensure employees know not to respond or click anything, and how to report such emails internally without embarrassment (e.g. via a confidential phishing-report button or hotline).
- Clear Reporting Channels: Make it easy and anonymous if necessary for employees to report sextortion attempts. An internal policy might state: “If you receive a suspected blackmail or scam email, forward it to security immediately.” This counters the tendency to hide such emails. As ESET advises, employees should notify IT even for work email sextortion.
- Incident Response Playbooks: Develop a runbook for sextortion incidents. Steps should include verifying claims (e.g. checking internal security logs to confirm no actual breach), isolating any involved systems, and instructing the employee to do things like change compromised passwords (preferably via a second channel). Engage corporate communications and legal if threats involve reputational risk. Always include: do not engage or negotiate with the attacker.
- Policy on Cryptocurrency Payments: Explicitly forbid employees from paying any ransom. Even if personal, paying emboldens attackers and provides no guarantee. The organization should have a zero-tolerance stance on extortion payments, and employees should be trained in this policy, as paying often worsens the situation.
- Privacy Protection & MFA: Reduce risk by minimizing leaked credential impact. Encourage or require the use of password managers so employees don’t reuse passwords between personal and work accounts. Enforce multi-factor authentication on all business systems. If a sextortion email mentions an old password, have the employee (or security team) reset any overlapping corporate credentials immediately.
Each recommendation combines technical measures (filters, monitoring, MFA) with human/policy measures (awareness, reporting culture). Together, they help break the Panic Attack Chain by reducing false signals and ensuring a rational, controlled response when an employee is targeted.
Final Thoughts and Next Steps
A sextortion email need not start as a technical breach to endanger an organization. By understanding the Panic Attack Chain and False Compromise Signals, security leaders can anticipate how personal blackmail can morph into corporate crisis. Key takeaways:
- Sextortion is not just personal: Over 10% of targeted phishing can involve sextortion tactics. Treat any employee report seriously.
- Victim behavior drives the outcome: Train staff to keep calm, not share, and report immediately.
- Bolster email defenses: Use specialized filters and AI to catch unusual extortion content.
- Build clear policies: Ensure employees know the exact steps to take (and not take) if they receive such a threat.
Organizations should review their email security posture in light of these threats. StrongestLayer’s Email Security and Threat Intelligence solutions can help detect and filter sophisticated social-engineering attacks.
Frequently Asked Questions (FAQs)
Q1: Can a sextortion email become an enterprise security incident?
Yes. A sextortion email does not need to compromise a corporate account or device to create enterprise risk. An employee may be targeted through personal information, leaked credentials, or publicly available details, and the resulting pressure can influence decisions involving corporate accounts, data, communications, or security procedures. The risk increases when attackers attempt to move the victim into additional communication channels or obtain credentials or authentication information.
Q2: Can sextortion emails affect employees even when their work accounts are secure?
Yes. A personal sextortion campaign can create a workplace security concern even when there is no evidence that the employee's corporate account was compromised. Security teams should distinguish personal targeting from corporate compromise while still checking whether leaked credentials, password reuse, or subsequent attacker contact could create an account-takeover pathway.
Q3: Why would a sextortion attacker target an employee's personal information?
Personal information can make an extortion attempt appear more credible. Names, addresses, employers, social profiles, family connections, and previously exposed credentials can be combined to create the impression that an attacker has extensive access. The presence of accurate personal information alone does not establish that the attacker has access to the victim's device or corporate environment.
Q4: What should a security team do when an employee reports a sextortion email?
The first priority is to preserve the evidence and assess whether there is any indication of an actual account or endpoint compromise. Security teams should retain the original message and relevant headers, identify whether credentials were exposed, check for related authentication activity, and determine whether the employee interacted with links, attachments, or requests for authentication information. If the incident involves criminal extortion or threats, the organization should also consider appropriate law-enforcement reporting. The FBI recommends preserving relevant communications and reporting sextortion activity.
Q5: Does a leaked password in a sextortion email mean the employee has been hacked?
No. A password appearing in a sextortion message can originate from an earlier data breach or credential exposure. It should therefore trigger verification rather than automatically being treated as proof of an active compromise. If the password is still in use anywhere, however, it represents a genuine security concern and should be changed immediately.
Q6: Can sextortion emails contain no malware and still be dangerous?
Yes. The absence of a malicious attachment, executable payload, or malicious link does not make a coercive email harmless. The attack can be designed around psychological manipulation and the recipient's subsequent actions. An employee who panics may disclose credentials, bypass normal procedures, transfer money, or reveal information that creates a separate security incident.
Q7: How can email security detect sextortion without relying on malware?
Detection can incorporate signals beyond traditional payload analysis, including sender identity, authentication anomalies, language associated with coercion or extortion, unusual requests, credential exposure, behavioral patterns, and relationships between the sender and recipient. This is particularly relevant for threats where the malicious element is the intent of the communication, rather than malicious code.
Q8: Should employees report sextortion emails to the security team?
Yes, particularly when the message reaches a corporate mailbox, references company information, contains a work credential, or creates any possibility of subsequent account compromise. Reporting also gives security teams an opportunity to identify whether similar messages are targeting other employees.
Q9: Should an employee pay a sextortion demand?
Paying does not provide a reliable resolution and can encourage further demands. Employees should preserve the evidence, avoid further engagement where appropriate, and follow the organization's incident-reporting process. Individuals who believe they are victims of criminal sextortion should also consider reporting it to the appropriate law-enforcement authority. The FBI advises sextortion victims to seek help and report the crime rather than handling the situation alone.
Q10: What is the biggest mistake organizations can make when handling sextortion?
Treating the incident as either purely personal or automatically a corporate breach.
The better approach is to investigate both possibilities.
The organization should determine whether the employee was simply targeted using personal information or whether the campaign intersected with corporate credentials, accounts, devices, data, or communication channels. That distinction allows security teams to respond proportionately without dismissing a potentially serious attack.
Subscribe to Our Newsletters!
Be the first to get exclusive offers and the latest news


Catches what your gateway approved.